

Production Builds
Reduce contract size and create reproducible builds that users can verify against the deployed code.
In this page, we will explore strategies for reducing the size of smart contracts on NEAR. This is particularly useful for developers who want to optimize their contracts for deployment, especially in scenarios where contract size limits are a concern.
Reducing a contract's size
Advice & examples
This page is made for developers familiar with lower-level concepts who wish to reduce their contract size significantly, perhaps at the expense of code readability.
Some common scenarios where this approach may be helpful:
- contracts intended to be tied to one's account management
- contracts deployed using a factory
- future advancements similar to the EVM on NEAR
There have been a few items that may add unwanted bytes to a contract's size when compiled. Some of these may be more easily swapped for other approaches while others require more internal knowledge about system calls.
Small wins
Using flags
When compiling a contract make sure to pass flag -C link-arg=-s to the rust compiler:
RUSTFLAGS='-C link-arg=-s' cargo build --target wasm32-unknown-unknown --release
Here is the parameters we use for the most examples in Cargo.toml:
[profile.release]
codegen-units = 1
opt-level = "s"
lto = true
debug = false
panic = "abort"
overflow-checks = true
You may want to experiment with using opt-level = "z" instead of opt-level = "s" to see if generates a smaller binary. See more details on this in The Cargo Book Profiles section. You may also reference this Shrinking .wasm Size resource.
Removing rlib from the manifest
Ensure that your manifest (Cargo.toml) doesn't contain rlib unless it needs to. Some NEAR examples have included this:
[!WARNING]
Adds unnecessary bloat
[lib]
crate-type = ["cdylib", "rlib"]
when it could be:
[!TIP]
[lib]
crate-type = ["cdylib"]
- When using the Rust SDK, you may override the default JSON serialization to use Borsh instead. See overriding interface serialization for more information and an example.
- When using assertions or guards, avoid using the standard
assertmacros likeassert!,assert_eq!, orassert_ne!as these may add bloat for information regarding the line number of the error. There are similar issues withunwrap,expect, and Rust'spanic!()macro.
Example of a standard assertion:
[!WARNING]
Adds unnecessary bloat
assert_eq!(contract_owner, predecessor_account, "ERR_NOT_OWNER");
when it could be:
[!TIP]
if contract_owner != predecessor_account {
  env::panic(b"ERR_NOT_OWNER");
}
Example of removing expect:
[!WARNING]
Adds unnecessary bloat
let owner_id = self.owner_by_id.get(&token_id).expect("Token not found");
when it could be:
[!TIP]
fn expect_token_found<T>(option: Option<T>) -> T {
  option.unwrap_or_else(|| env::panic_str("Token not found"))
}
let owner_id = expect_token_found(self.owner_by_id.get(&token_id));
Example of changing standard panic!():
[!WARNING]
Adds unnecessary bloat
panic!("ERR_MSG_HERE");
when it could be:
[!TIP]
env::panic_str("ERR_MSG_HERE");
Ready to use script
We have prepared a simple bash script that can be used to minify .wasm contract file. You can find it here.
The current approach to minification is the following:
- Snip (i.e. just replace with unreachable instruction) few known fat functions from the standard library (such as float formatting and panic-related) with
wasm-snip. - Run
wasm-gcto eliminate all functions reachable from the snipped functions. - Strip unneeded sections, such as names with
wasm-strip. - Run
binaryen wasm-opt, which cleans up the rest.
Requirements to run the script:
cargo install wasm-snip wasm-gc
- install binaryen and wabt on your system. For Ubuntu and other Debian based Linux distributions run:
apt install binaryen wabt
[!CAUTION]
Minification could be rather aggressive, so you must test the contract after minification. Standalone NEAR runtime could be helpful here.
Lower-level approach
For a no_std approach to minimal contracts, observe the following examples:
- Tiny contract
- NEAR ETH Gateway
- This YouTube video where Eugene demonstrates a fungible token in
no_stdmode. The code for this example lives here. - Examples using a project called
nesdie. - Note that Aurora has found success using rjson as a lightweight JSON serialization crate. It has a smaller footprint than serde which is currently packaged with the Rust SDK. See this example of rjson in an Aurora repository, although implementation details will have to be gleaned by the reader and won't be expanded upon here. This nesdie example also uses the miniserde crate, which is another option to consider for folks who choose to avoid using the Rust SDK.
[!NOTE]
Information on system calls
The
near_syscrate exposes the low-level host functions available to contracts that interact directly with the runtime. See its reference for function signatures.The SDK's
envmodule provides higher-level wrappers around these functions.
Reproducible builds
Reproducible builds let different people build the same program and get the exact same output. They help users verify that a deployed contract corresponds to its published source code.
Building the same contract on different machines can produce similar but non-identical binaries because the artifact can be affected by the locale, timezone, build path, and other parts of the build environment. NEAR addresses this with NEP-330 source metadata, cargo-near, Docker, and SourceScan.
[!NOTE]
You need Docker to use the reproducible-build workflow.
When you initialize a project with cargo near new, its Cargo.toml includes the build environment and repository metadata:
repository = "https://github.com/<organization>/<repository>"

[package.metadata.near.reproducible_build]
image = "sourcescan/cargo-near:0.13.5-rust-1.85.1"
image_digest = "sha256:3b0272ecdbb91465f3e7348330d7f2d031d27901f26fb25b4eaf1560a60c20f3"
passed_env = []
container_build_command = [
    "cargo",
    "near",
    "build",
    "non-reproducible-wasm",
    "--locked",
]
When you deploy with cargo near deploy, this information is used to clone the repository and compile the contract in a Docker container. The build adds a contract_source_metadata method without changing the contract's logic.
After deployment, inspect that metadata with:
near view <contract-account> contract_source_metadata
Verify and publish
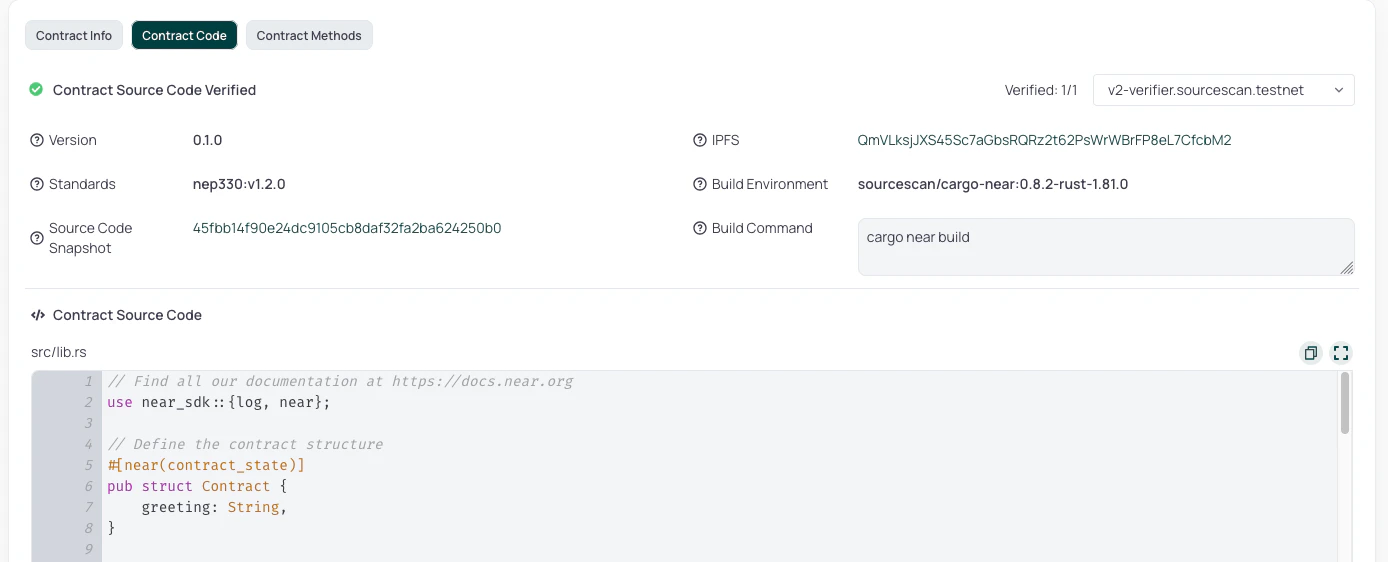
To verify and publish the contract's code, open its account page in NearBlocks, select the Contract tab, and use Verify and Publish. After verification, the source and metadata are available under Contract → Contract Code.
For a complete walkthrough, see the SourceScan verification guide.